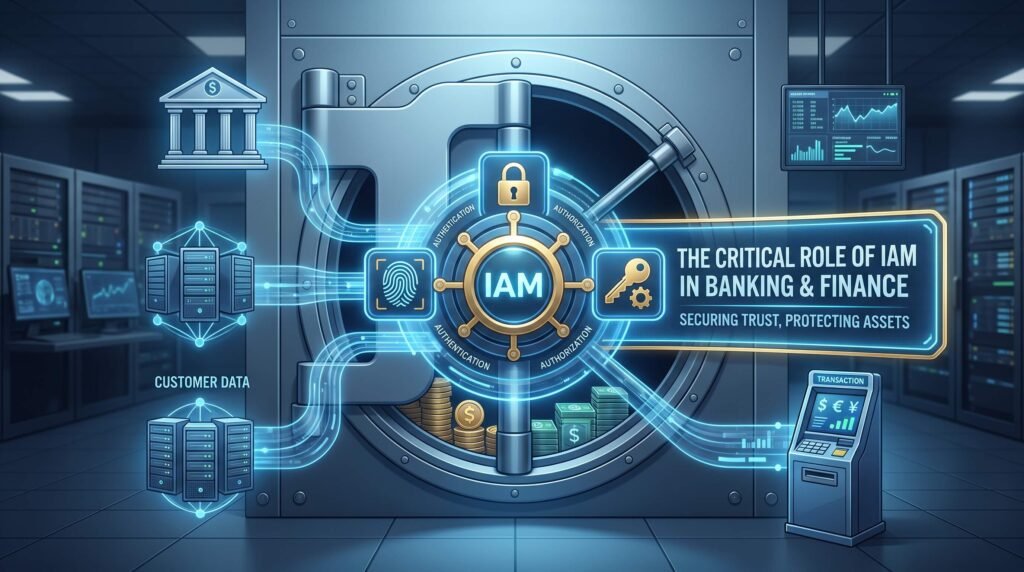
A teller in a mid-sized Saudi bank branch resigns on a Sunday. By Tuesday, her domain account is still active, her core-banking system access is still live, and her mobile-approval app still lets her authorize wire transfers. Nobody flagged it — because the bank’s onboarding and offboarding process runs on emails and spreadsheets, not automation. Three weeks later, that dormant account is used to move funds. This is not fiction; it is the exact scenario IAM in banking is designed to prevent.
Financial institutions carry a unique burden: they hold the most sensitive data in the economy, they are bound by the strictest regulations, and they are the most attractive target for both external attackers and insider fraud. IAM in banking is not a “nice to have” security layer — it is the operational backbone that determines whether a bank can prove, at any moment, exactly who has access to what, and why.
Why Banks Need IAM More Than Any Other Sector
Retail and manufacturing companies can often tolerate a delayed offboarding or an over-permissioned account for a few days. Banks cannot. Every account with access to core banking, SWIFT messaging, or customer financial records is a potential fraud vector. IAM in banking addresses this by enforcing least-privilege access, automated de-provisioning, and continuous monitoring of who touches sensitive systems.
“Read Also: Best Practices for Managing Active Directory in Modern Enterprises“
Protecting Financial Data at Scale
A Saudi bank with branches in Riyadh, Jeddah, and the Eastern Province may manage tens of thousands of employee and contractor identities, each tied to multiple applications: core banking platforms, CRM systems, treasury tools, and internal portals. Without centralized IAM in banking, each system manages its own access independently — creating blind spots where an employee’s access in one system is never reviewed against their actual job function in another. Centralized identity governance closes that gap by giving security teams a single, authoritative view of every identity and every entitlement across the bank.
Regulatory Compliance: SAMA and NCA Requirements
The Saudi Central Bank (SAMA) Cyber Security Framework and the National Cybersecurity Authority’s Essential Cybersecurity Controls both place identity governance at the heart of their requirements — access certification, segregation of duties, privileged account monitoring, and detailed audit trails are not optional line items, they are examined directly. IAM in banking gives institutions the tooling to generate these audit trails automatically, rather than reconstructing them manually before every examination, which is both risky and resource-intensive.
“Read More About: SAMA Compliance Audit Requirements: Guide for KSA Entities“
Preventing Internal and External Fraud
Insider fraud is often harder to detect than external attacks because the access being misused is technically “authorized.” Strong IAM in banking mitigates this through segregation-of-duties controls — ensuring, for example, that the person who initiates a wire transfer cannot also be the person who approves it — combined with continuous access reviews that catch privilege creep before it becomes a liability. On the external side, IAM reduces the attack surface by enforcing multi-factor authentication and monitoring for anomalous login behavior across branches and digital channels.
The Business Case Beyond Compliance
Beyond satisfying regulators, mature IAM in banking accelerates operations. New hires and contractors get access to exactly what they need on day one instead of waiting days for manual provisioning. Auditors get self-service reports instead of ad-hoc data pulls. And when a role changes — a common occurrence in banking as staff rotate between branches and departments — access updates automatically instead of accumulating as forgotten, unused permissions.
Conclusion
For Saudi banks and financial institutions, IAM in banking is not a technology project — it is risk management, regulatory survival, and operational efficiency rolled into one discipline. The institutions that invest in mature identity governance today are the ones that will move fastest through SAMA and NCA audits tomorrow, while quietly closing the door on the fraud vectors that keep CISOs awake at night.
Ready to strengthen your bank’s identity and access management posture? We help Saudi financial institutions design, implement, and audit IAM frameworks that satisfy SAMA and NCA requirements while reducing fraud risk. Contact us for a compliance consultation tailored to the banking sector.
contact@cyber-aman.com