When a Saudi insurance company finally ran its first formal access review, the results were sobering: 22% of all active permissions across core systems belonged to employees who no longer needed them — some tied to roles they’d left two years earlier. Nobody had done anything malicious; access had simply never been reviewed. This is exactly the gap that structured access certification campaigns, run as part of a broader identity governance program, are designed to close.
What Access Certification Campaigns Actually Are
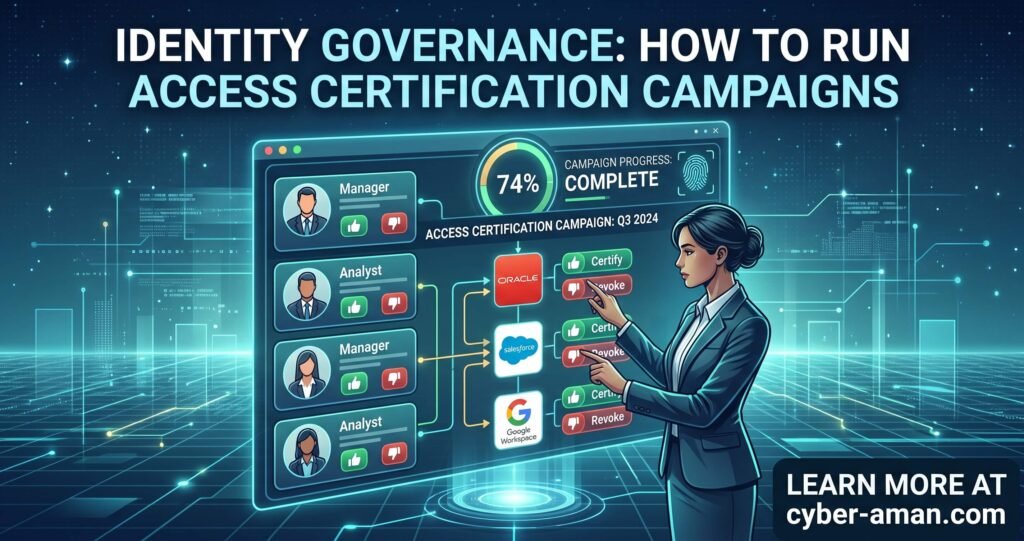
Access certification campaigns are periodic, structured reviews in which managers, application owners, or data owners formally confirm — or revoke — the access each user holds. Rather than IT deciding unilaterally what access is appropriate, identity governance shifts that responsibility to the people who actually understand whether an employee still needs a given permission for their current role.
Why Ad-Hoc Reviews Don’t Work
Many organizations attempt access reviews informally — an email asking managers to “check their team’s access” once a year, with no structure, no deadline enforcement, and no audit trail. This approach almost always produces low completion rates and rubber-stamp approvals, because reviewers are given no context about what each permission actually grants. Genuine identity governance requires structured campaigns with clear scope, deadlines, and escalation.
“Read More: Enhancing User Experience and Security with (SSO)“
Designing an Effective Campaign
Effective access certification campaigns within an identity governance program share several traits: they are scoped clearly (by application, department, or risk tier rather than reviewing everything at once), they provide reviewers with meaningful context (what does this permission actually allow, and when was it last used), and they set firm deadlines with automated reminders and escalation to a reviewer’s manager if ignored.
A common and effective approach for Saudi enterprises is a risk-tiered model: privileged and financial-system access reviewed quarterly, standard application access reviewed semi-annually, and low-risk access (like shared read-only resources) reviewed annually.
Involving the Right Reviewers
Identity governance programs fail when the wrong person is asked to certify access. A direct manager, not a central IT team, should certify whether an employee still needs access relevant to their day-to-day role, while application or data owners should certify access to the specific systems they are accountable for — since they understand the sensitivity and appropriate scope far better than a generic reviewer would.
Turning Reviews Into Action
A certification campaign only delivers value if revoked access is actually removed — a step many organizations struggle with operationally. Mature identity governance platforms automate this final step, feeding certification decisions directly into provisioning workflows so that a “revoke” decision triggers automatic removal from the relevant AD group or application, rather than generating another manual ticket that sits unactioned for weeks.
“Read Also: Implementing Self-Service Password Reset (SSPR) AD Users“
Compliance and Audit Value
For Saudi enterprises operating under NCA Essential Cybersecurity Controls or sector-specific frameworks like SAMA, documented access certification campaigns are frequently a direct audit requirement — auditors want to see not just that access is appropriate today, but that it is reviewed on a defined, recurring cadence, with evidence of reviewer accountability and completion tracking.
Conclusion
Access certification campaigns are where identity governance moves from theory into measurable risk reduction. Run consistently, with the right reviewers and real consequences for revoked access, they close the gap between the access employees actually need and the access they’ve quietly accumulated over time.
Ready to launch a structured access certification program? We help Saudi enterprises design and implement identity governance frameworks, including access certification campaigns aligned with NCA and sector-specific compliance requirements. Contact us to get started.