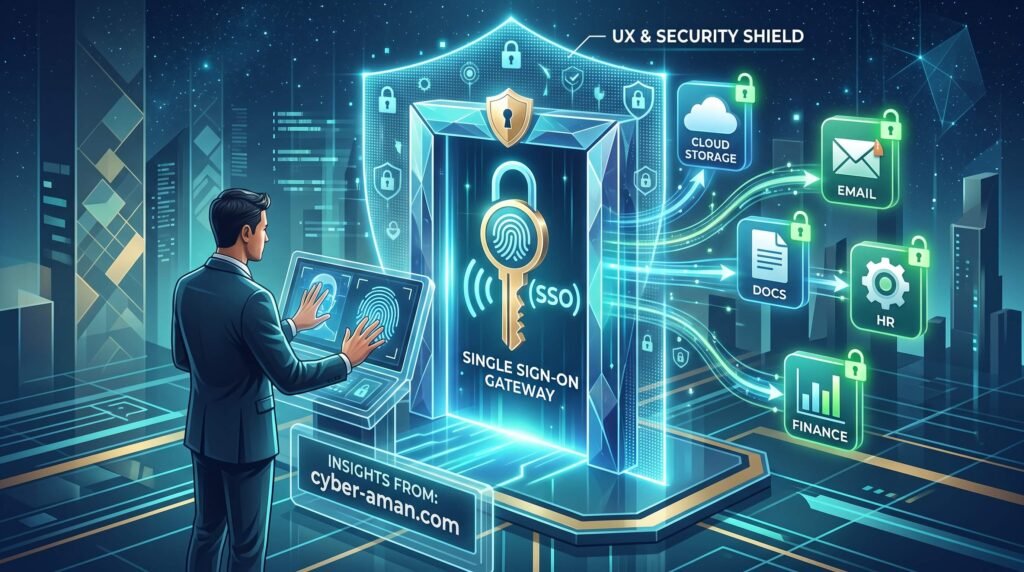
Ask any employee at a mid-sized Saudi enterprise how many passwords they manage for work, and the honest answer is usually somewhere between eight and fifteen — email, ERP, HR portal, expense system, CRM, internal wiki, and more. Many simply reuse the same password everywhere, or write them down, because remembering fifteen unique passwords is unrealistic. Single Sign-On (SSO) exists precisely to eliminate this problem, replacing that sprawl with one strong credential and one login experience.
What Single Sign-On Actually Solves
Single Sign-On (SSO) allows a user to authenticate once — typically through a centralized identity provider — and gain access to every connected application without logging in again. Beyond the obvious convenience, this directly addresses a major security weakness: password reuse. When employees only need to remember one strong password instead of a dozen weak, reused ones, the organization’s overall credential-based attack surface shrinks significantly.
The User Experience Impact
For a retail company in Jeddah running a busy customer-service floor, every extra login screen is lost productive time multiplied across hundreds of staff, every single day. Single Sign-On removes that friction entirely — staff log in once at the start of their shift and move fluidly between the CRM, ticketing system, and internal knowledge base without re-authenticating, which measurably improves both morale and productivity in high-volume environments.
“Read Also: Secure Password Delivery Mechanisms for New Hires and Resets“
Strengthening Security, Not Just Convenience
A common misconception is that Single Sign-On (SSO) trades security for convenience. In reality, well-implemented SSO strengthens security: it becomes far easier to enforce strong multi-factor authentication at a single point, centrally revoke access the instant an employee leaves (since disabling one account cuts off every connected application), and monitor login behavior for anomalies across the entire application portfolio from a single point of visibility.
How SSO Fits Into a Broader IAM Strategy
Single Sign-On rarely stands alone — it works best as part of a broader identity and access management strategy that includes centralized user provisioning, role-based access, and MFA. A Saudi logistics company integrating Single Sign-On with its identity governance platform, for example, gains the added benefit of every application login event feeding into a single audit trail, simplifying compliance reporting considerably.
Implementation Considerations for Saudi Enterprises
Rolling out Single Sign-On (SSO) across an enterprise with a mix of modern SaaS applications and legacy on-premises systems requires careful protocol planning — SAML and OAuth/OIDC cover most modern applications, while older legacy systems may need an identity bridge or agent-based integration. Enterprises should also plan for Arabic-language login interfaces and ensure the SSO provider supports the specific compliance and data residency requirements relevant to their sector.
“Read Also: Implementing Self-Service Password Reset (SSPR) AD Users“
Common Pitfalls to Avoid
Organizations occasionally treat Single Sign-On as a purely technical project, skipping change management — leading to confused users during rollout and a spike in helpdesk tickets. A phased rollout, clear communication, and pairing SSO launch with self-service password reset tends to produce a far smoother transition than a single big-bang cutover across the whole organization.
Conclusion
Single Sign-On (SSO) is one of the rare security investments that genuinely improves the daily experience of every employee while simultaneously strengthening the organization’s security posture. For Saudi enterprises juggling growing application portfolios, it is quickly becoming a baseline expectation rather than a luxury.
Ready to simplify login and strengthen security across your applications? We help organizations design and deploy Single Sign-On solutions integrated with their existing IAM and Active Directory environment. Contact us to explore your options.