For decades, enterprise security worked like a castle: strong walls around the perimeter, and relative trust for anyone already inside. That model collapsed the moment remote work, cloud applications, and mobile devices became the norm — there is no longer a single perimeter to defend. This is exactly why IAM Zero Trust architecture has become the dominant security model for modern Saudi enterprises: when there’s no perimeter left to trust, identity becomes the new control point.
What “Never Trust, Always Verify” Actually Means
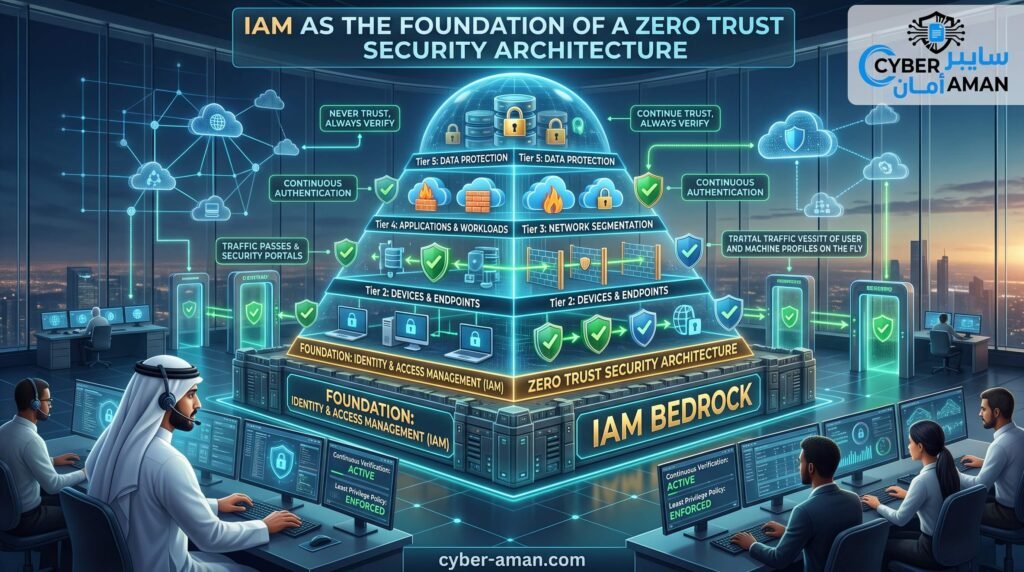
The Zero Trust philosophy assumes no user, device, or application should be trusted by default — regardless of whether the request originates inside or outside the traditional network boundary. Every access request must be verified explicitly, every time. IAM Zero Trust architecture is what makes this actually enforceable, because identity — not network location — becomes the primary signal used to grant or deny access.
Why IAM Is the Foundation, Not Just a Component
Many security tools contribute to a Zero Trust model — network segmentation, endpoint detection, encryption — but IAM Zero Trust architecture sits underneath all of them, because every one of those controls ultimately needs to answer the same question: who is this, and should they have access to this specific resource, right now? Without strong identity verification and governance, every other Zero Trust control is built on an unreliable foundation.
“Read More: Identity Governance: How to Run Access Certification Campaigns“
Core IAM Capabilities That Enable Zero Trust
Several IAM capabilities are essential building blocks of IAM Zero Trust architecture: strong multi-factor authentication for every access request, not just initial login; continuous, risk-based evaluation of context — device health, location, time of day, and behavior — rather than a one-time login check; least-privilege access enforced through role-based or attribute-based controls; and centralized identity governance that keeps access current as roles and employment status change.
A Practical Saudi Enterprise Example
Consider a Saudi oil and gas services company with field engineers accessing systems remotely from drilling sites, office staff working hybrid schedules, and contractors requiring temporary access. Under IAM Zero Trust architecture, each access request is evaluated on its own merits — a field engineer’s device health and location are checked before granting access to operational systems, regardless of whether they’re connecting from the office network or a remote site, because network location alone no longer implies trust.
Moving Beyond the VPN Mindset
Many organizations still rely heavily on VPNs as their primary security boundary — granting broad network access once a VPN connection is established. IAM Zero Trust architecture replaces this with application-level, identity-based access: a user authenticates and is granted access only to the specific applications and resources their role requires, not to the entire network, significantly limiting what an attacker could reach even with a compromised credential.
“Read Also: Enhancing User Experience and Security with (SSO)“
Implementation Roadmap
Organizations adopting IAM Zero Trust architecture typically start by strengthening core identity foundations — MFA everywhere, centralized identity governance, and clean Active Directory hygiene — before layering in continuous risk evaluation and micro-segmentation. Attempting to implement Zero Trust network controls without first maturing the underlying IAM foundation is one of the most common reasons Zero Trust initiatives stall or underdeliver.
Conclusion
As Saudi enterprises continue adopting cloud services, remote work, and increasingly complex application ecosystems, the perimeter-based security model no longer holds. IAM Zero Trust architecture provides the identity-centric foundation that makes “never trust, always verify” achievable in practice, not just as a security slogan.
Ready to build your Zero Trust strategy on a strong IAM foundation? We help Saudi enterprises design and implement IAM-centered Zero Trust architectures. Contact us to discuss your security roadmap.