In nearly every major breach investigation, the same pattern emerges: an attacker gains an initial, low-level foothold, then escalates to a privileged administrator account — and from there, the entire environment is theirs. This is why security professionals call privileged accounts “the keys to the kingdom,” and why Privileged Access Management (PAM) has become one of the highest-priority investments for enterprises across Saudi Arabia, from banking to healthcare to government.
Why Privileged Accounts Are the Highest-Value Target
A standard user account can typically only damage its own limited scope of access. A domain administrator account, a database root account, or a network device admin credential can touch nearly everything. Privileged Access Management (PAM) exists specifically because these accounts carry disproportionate risk relative to their small number — often less than 5% of all accounts in an organization, yet responsible for the vast majority of catastrophic breach scenarios.
Credential Vaulting: The Foundation of PAM
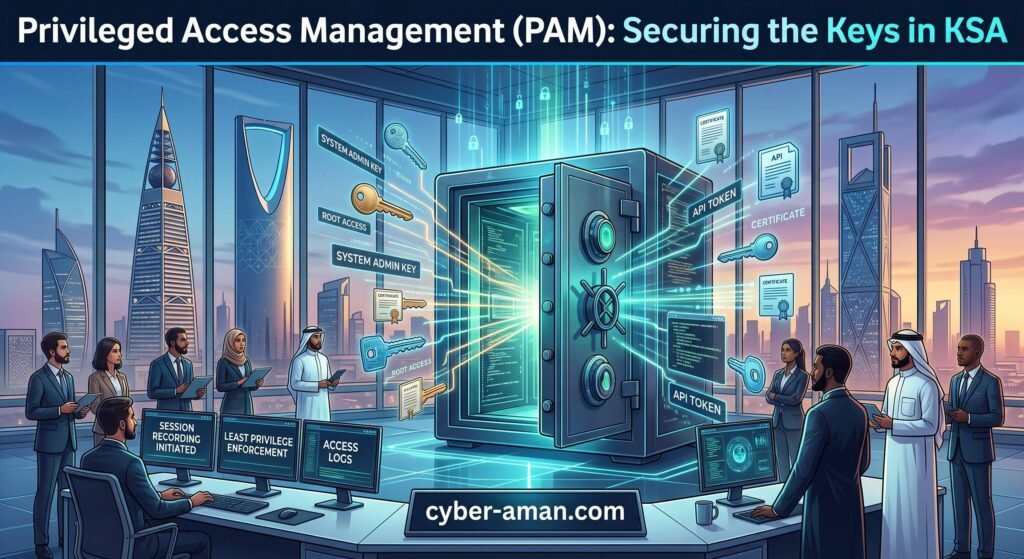
At its core, Privileged Access Management (PAM) starts with vaulting — storing privileged credentials in an encrypted, access-controlled repository rather than allowing administrators to know or manage static passwords themselves. When an administrator needs to perform a privileged task, they request temporary access through the PAM platform, which checks out the credential, logs the request, and can rotate the password automatically afterward — meaning no human ever needs to memorize or share the actual password.
Session Monitoring and Recording
Beyond vaulting, mature Privileged Access Management (PAM) implementations monitor and record privileged sessions in real time — capturing exactly what commands an administrator ran, what files they accessed, and what changes they made during a privileged session. For a Saudi financial institution under SAMA oversight, this session-level audit trail is often a direct compliance requirement, not just a security nice-to-have, since regulators expect institutions to demonstrate exactly what privileged users did and when.
“Read More: Securing Workstations: MFA for Endpoints“
Just-in-Time Access Over Standing Privileges
Traditional environments grant administrators standing, always-on privileged access — a significant risk, since a compromised admin account is immediately capable of maximum damage at any moment. Modern Privileged Access Management (PAM) shifts toward just-in-time access, where elevated privileges are granted only for the duration of an approved task and automatically revoked afterward, dramatically shrinking the window an attacker could exploit even if a privileged credential were compromised.
Real-World Implementation: Beyond IT Administrators
Privileged Access Management (PAM) isn’t limited to IT staff. Database administrators, network engineers, third-party vendors performing maintenance, and even certain business users with elevated financial system access all fall within its scope. A company compliance mapping exercise, for example, typically covers dozens of controls spanning discovery of privileged accounts, onboarding into the vault, password policy enforcement, session control, and detailed reporting — reflecting just how broad a mature PAM program needs to be.
Common Implementation Challenges
Organizations implementing Privileged Access Management (PAM) often underestimate the discovery phase — finding every privileged account across the environment, including forgotten service accounts and shared credentials that predate current staff. A thorough discovery and onboarding process, done methodically rather than rushed, is what determines whether a PAM rollout actually closes the risk gap or simply vaults the accounts everyone already knew about.
Conclusion
Privileged Access Management (PAM) directly addresses the single highest-risk category of access in any enterprise. By vaulting credentials, monitoring sessions, and shifting toward just-in-time access, Saudi organizations can dramatically reduce the blast radius of a compromised administrator account — often the difference between a contained incident and a full-scale breach.
Looking to implement or strengthen your Privileged Access Management program? We specialize in PAM implementation, including PAM360 deployments and compliance mapping for Saudi enterprises. Contact us for a consultation.